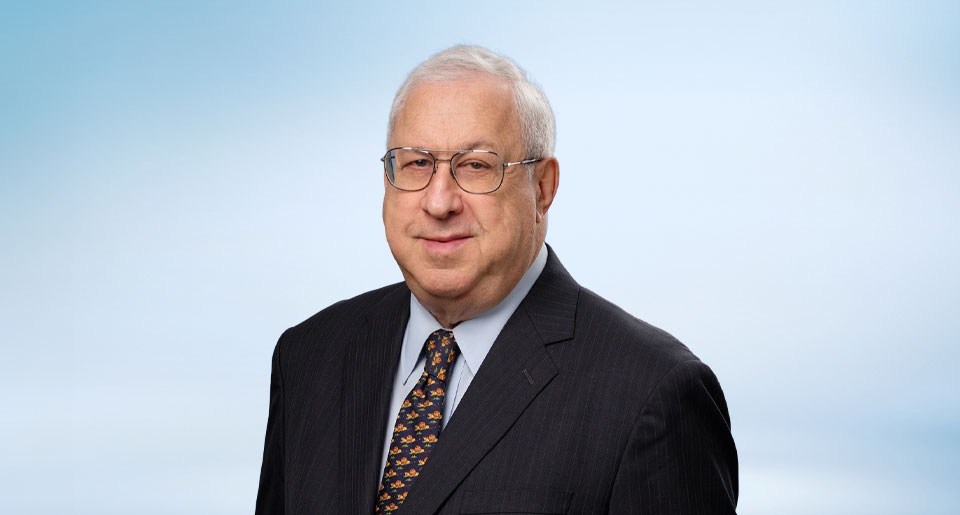
Portrait of Stephen Siller

Stephen Siller

Principal

Stephen Siller anticipates and solves for international and domestic clients' business and legal issues, whether involving corporate law, mergers and acquisitions or other disciplines. He has completed more than 120 mergers and acquisitions transactions. His clients range from multinational manufacturing and trading companies to firms in the hospitality, logistics, distribution, commodities trading, staffing, real estate, banking, pharmacy benefits, media, equipment leasing and consulting fields.

Stephen has served on the American Bar Association Negotiated Acquisition Committee’s Task Force, which was responsible for drafting the ABA’s model form of Asset Purchase Agreement and Commentary.

Stephen also holds teaching positions in Business Law at New York University Stern School of Business MBA Program and Polytechnic Institute MBA Program.

    Education

    • Brooklyn Law School (J.D., cum laude)
    • New York University School of Law (LL.M.)
    • Brooklyn College, CUNY (B.A.)

    State Bar Admissions

    • New York

    Professional Affiliations

    • Vistage, Member
    • IR Global, Member
    • International Bar Association, Member
    • Negotiated Acquisitions Committee, American Bar Association, Member
    • Committee on Partnerships and Unincorporated Business Organizations, Member
    • Association of the Bar of the City of New York, Member
    • Transportation Committee, United States in the Global Economy, Member
    • Cape Classics, Inc., a South African fine-wine importer, Chairman, 1994 – 2007

    Recognitions

    • Selected to New York Metro Super Lawyers® or Business/Corporate, Mergers & Acquisitions, and International Law (2007–2010, 2013)
    • AV Preeminent® Rated, Martindale-Hubbell
    • Who's Who in America (2000–2001, 2003–2005, 2008–2012)
    • Who's Who in American Law (1985–1988, 1990–2008)
    • Who's Who in the World (2000)
    • Who's Who in the East (1999–2000)
    • Who's Who in Finance and Industry (1992–1995)
    • Who's Who of Emerging Leaders in America (1987–1994)
Firm Highlights

  • Events
    AIA Tri-State Conference
    Princeton will serve as the backdrop for three days of connection, learning, and design leadership. From keynotes to tours to the Tri-State Design Awards, this year’s conference is designed to go far beyond education sessions. Kick off the week with pre-conference intensives and individual state component Design Award celebrations, followed by three days of education, inspiration, networking, and design excellence at the 2026 AIA Tri-State Conference—featuring pre-conference intensives, three keynote speakers, 25 education sessions, curated tours, an expo, spec academies, and the AIA Tri-State Design Awards—bringing together architects and design professionals from New Jersey, New York, and Pennsylvania to connect, learn, and celebrate the best of the profession. G2. Designing Secure Practices: Cybersecurity, Data Privacy, Contractual Provisions, and Insurance Risks for Architects (4:00 PM - 5:30 PM) Architects and design professionals increasingly rely on cloud platforms, BIM software, and digital tools to manage sensitive data, creating cybersecurity and privacy risks. A single incident can trigger liability claims, regulatory obligations, reputational harm, and insurance challenges. Yet many firms underestimate how contracts, insurance, and internal practices intersect during a breach. This program offers legal and insurance perspectives on cyber risk in architecture, examining liability exposure, risky contract provisions, and mitigation strategies. A cyber insurance expert will explain policy responses, coverage gaps, coordination with professional liability, and best practices for aligning insurance with contractual risk and protecting firms from evolving cyber threats. Learning Objectives: Identify key cybersecurity and data privacy risks faced by architecture firms and explain how these risks can impact professional liability and project outcomes. Analyze common contractual provisions to determine which clauses may increase exposure to cyber incidents and propose strategies to mitigate these risks. Evaluate the scope and limitations of cyber insurance policies, including coordination with professional liability coverage, to determine how a policy would respond in a breach scenario. Develop actionable risk management strategies by integrating legal, contractual, and insurance considerations to protect sensitive client and project data.