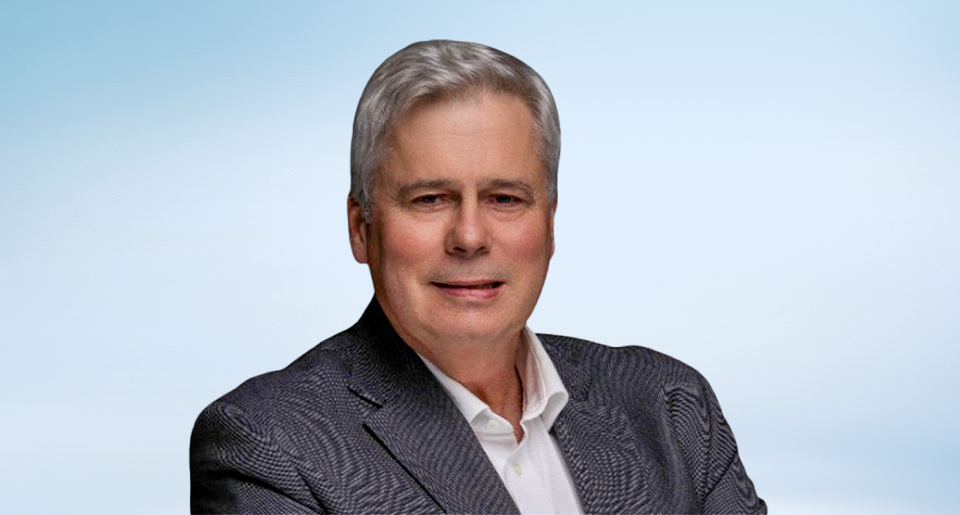
Scott Tobin provides strategic legal and business counsel to high‑growth companies and the boards, executives, and investors who guide them. His work centers on helping organizations manage risk while positioning for growth—especially at moments when decision‑making is time‑sensitive, and the stakes are high such as when raising capital, forming strategic partnerships, entering new markets, or planning for leadership transitions.
Drawing on a career that blends private practice with extensive in‑house and executive leadership experience, Scott advises clients on business growth and succession planning, board governance, strategic partnerships and licensing arrangements, mergers and acquisitions, and emerging company and venture capital matters. Clients also turn to him when disputes arise. His corporate litigation experience includes matters involving private company investors, lenders, directors, members, and management, and during election cycles, he has litigated election law disputes.
A significant portion of Scott's practice supports privately held technology companies and their investors, as well as businesses across a broad range of industries. He works closely with founders and leadership teams as owners, managers, or executives join or exit a business, and as companies evaluate how to leverage capital and technology to scale operations. In addition, he serves as U.S. general counsel to expansion‑minded domestic and overseas companies, advising on U.S. market entry and growth strategy.
Scott’s perspective is shaped by a longstanding record of leadership roles that extend well beyond traditional legal practice. During the late‑1990s internet boom, he left private practice to serve as general counsel and lead the successful sale of a longtime software client to a New York Stock Exchange–listed company. Before returning to private practice, he spent more than a decade as a principal and manager of entrepreneurial business ventures.
Over the course of his career, Scott has served as a board member, president, general counsel, and chief financial officer of an early AI‑focused, publicly traded molecular diagnostics company, as CEO and lead investor of a formerly NASDAQ‑listed North Carolina furniture manufacturer, as general counsel to a global software company, and as an executive vice president overseeing global strategy and venture investment initiatives for a New York Stock Exchange‑listed enhanced communications technology company. His legal career has also included service as the Atlanta managing partner of a European‑headquartered law firm and as an Assistant Attorney General for the State of Georgia.
- University of North Carolina School of Law (J.D.)
- University of North Carolina at Chapel Hill (B.A.)
- Georgia
- North Carolina
- Angel Capital Association, Member
- Association for Corporate Growth, Raleigh-Durham Chapter, Public Policy Task Force Co-Chair, Former Board Member
- National Association of Corporate Directors, Certified Director, Research Triangle Chapter, Board Member and Past Chair
- Piedmont Triad Entrepreneurial Network, Former Board Member
- Republican National Lawyers Association, Member
- RTP Capital, Member
- RTP Capital, Member
- Rotary Club, Paul Harris Fellow
- Savannah Economic Development Authority Creative Coast Alliance, Former Advisory Board Member
- State Bar of Georgia, Member
- State Bar of North Carolina, Member
- UNC School of Law Alumni Association, Board Member and Former Executive Committee Member
- UNC School of Law Council for Entrepreneurial Law, Former Director
- UNC School of Law Foundation, Former Board Chair and President
- UNC School of Law Initiative for Corporate Governance, Former Co-Managing Director
- UNC School of Law Long Range Planning Committee, Past Chair
- UNC School of Law William Horn Battle Society, Member
- Best Lawyers in America®, 2024
- Martindale-Hubbell AV® Preeminent™ Peer Review