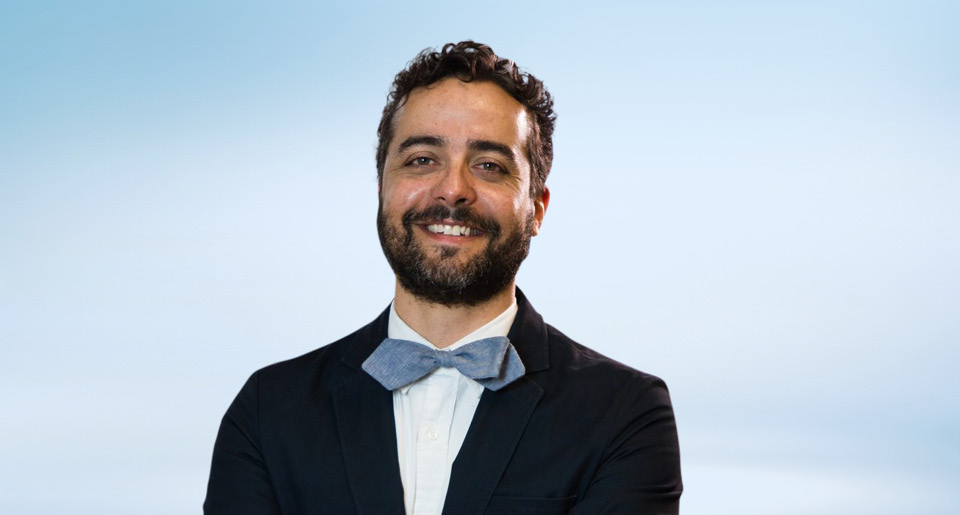
Portrait of Greg Grissett

Gregory Grissett

Principal

Gregory Grissett is a medical device patent strategist and helps medical device enterprises protect their innovations, minimize intellectual property (IP) related risk, enforce patents and defend against patent assertions. Gregory does this primarily through patent preparation and procurement, post-grant proceedings (IPR, ex parte reexaminations), patent litigation and various types of patent analysis. In addition, Gregory routinely advises companies on technology transactions through drafting and negotiating joint development agreements, software development and service agreements and licenses for all forms of IP. Gregory has significant experience assisting businesses with IP related to cardiovascular devices, orthopedics (ACL repair and reconstruction), catheters, heart valves, collagen implants, biologics, sutures & suture deployment instruments, robotics, embedded IoT medical devices, SaMD (software as a medical device) and diagnostics.

Gregory has a rare combination of experience in the international and business aspects of IP. He lived and worked in Paris, France, where he gained experience in U.S. and European patent procurement and enforcement. He also has business experience working with major global corporations in IP management and licensing roles. Gregory’s international perspective and practical experience help medical device innovators proactively manage IP development and enforcement issues unique to complex business operations.

    Education

    • North Carolina Central University School of Law (J.D.)
    • North Carolina State University (M.S.)
      • Textile Technology
    • North Carolina State University (B.S.)

    State Bar Admissions

    • North Carolina

    Court Admissions

    • United States Patent and Trademark Office
  • Biography
  • Representative Matters
  • Offit Kurman Blogs
  • Publications & News

Firm Highlights

  • Events
    AIA Tri-State Conference
    Princeton will serve as the backdrop for three days of connection, learning, and design leadership. From keynotes to tours to the Tri-State Design Awards, this year’s conference is designed to go far beyond education sessions. Kick off the week with pre-conference intensives and individual state component Design Award celebrations, followed by three days of education, inspiration, networking, and design excellence at the 2026 AIA Tri-State Conference—featuring pre-conference intensives, three keynote speakers, 25 education sessions, curated tours, an expo, spec academies, and the AIA Tri-State Design Awards—bringing together architects and design professionals from New Jersey, New York, and Pennsylvania to connect, learn, and celebrate the best of the profession. G2. Designing Secure Practices: Cybersecurity, Data Privacy, Contractual Provisions, and Insurance Risks for Architects (4:00 PM - 5:30 PM) Architects and design professionals increasingly rely on cloud platforms, BIM software, and digital tools to manage sensitive data, creating cybersecurity and privacy risks. A single incident can trigger liability claims, regulatory obligations, reputational harm, and insurance challenges. Yet many firms underestimate how contracts, insurance, and internal practices intersect during a breach. This program offers legal and insurance perspectives on cyber risk in architecture, examining liability exposure, risky contract provisions, and mitigation strategies. A cyber insurance expert will explain policy responses, coverage gaps, coordination with professional liability, and best practices for aligning insurance with contractual risk and protecting firms from evolving cyber threats. Learning Objectives: Identify key cybersecurity and data privacy risks faced by architecture firms and explain how these risks can impact professional liability and project outcomes. Analyze common contractual provisions to determine which clauses may increase exposure to cyber incidents and propose strategies to mitigate these risks. Evaluate the scope and limitations of cyber insurance policies, including coordination with professional liability coverage, to determine how a policy would respond in a breach scenario. Develop actionable risk management strategies by integrating legal, contractual, and insurance considerations to protect sensitive client and project data.